Ethical Hacking & Penetration Testing

–

(Security Audits)

I provide authorized security testing to help teams understand risk across web applications, networks, and cloud environments. Each assessment begins with written authorization and agreed rules of engagement. Findings are documented with context and practical remediation guidance.
Scope Web/API, Network, Cloud, Mobile
Standards OWASP Top 10, NIST, PCI DSS
Focus Vulnerability Assessment & Remediation Guidance
Engagement standard Written authorization and agreed rules of engagement
Abstract graphic representing a digital audit or penetration test
Cybersecurity work portfolio visual

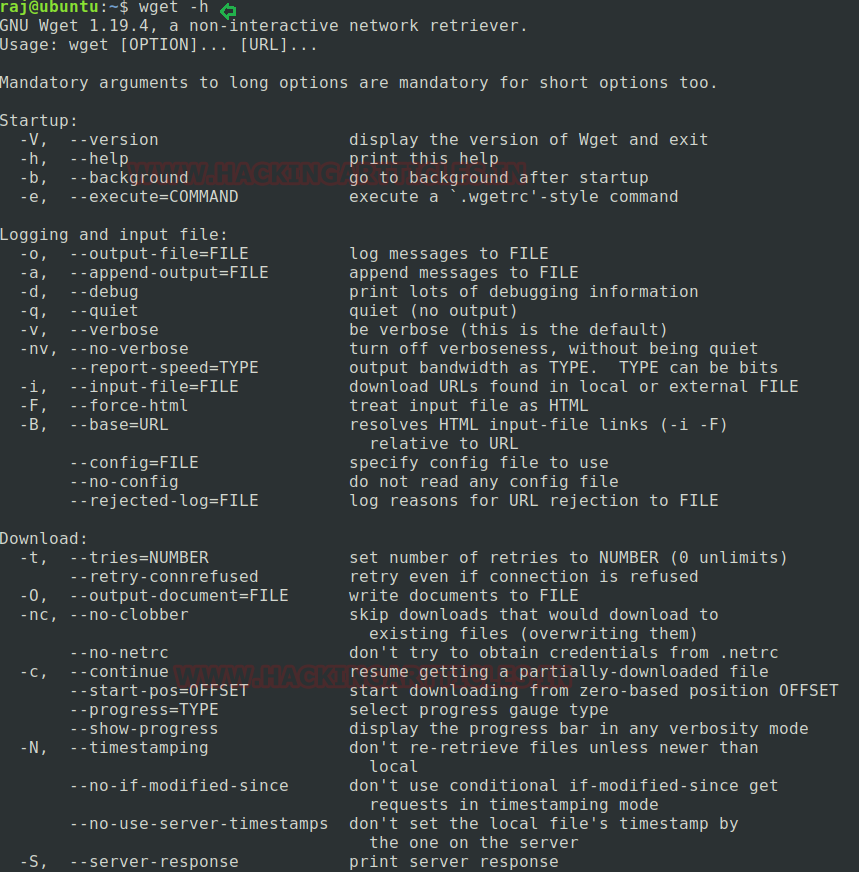
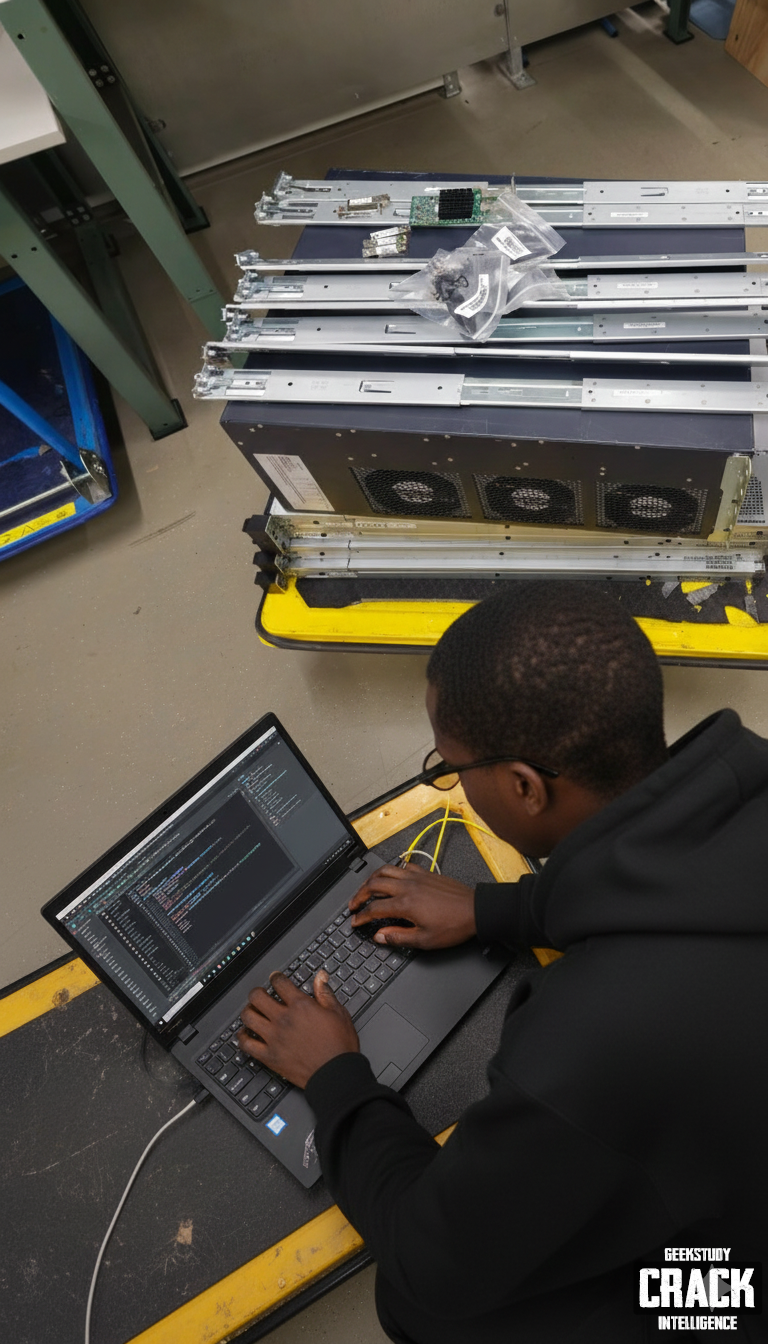
Demonstration of successful exploitation and evidence collection during a network penetration test.

(Pentest Process)

Start with agreed objectives, asset boundaries, and threat assumptions. Testing can combine manual review with references such as OWASP guidance to assess common web, API, identity, and configuration risks.
Validate findings only to the level permitted by the rules of engagement. Reports explain evidence, likely impact, and practical remediation options so teams can prioritize follow-up work.
Cybersecurity work portfolio visual

(Tool Mastery)

Assessment Phase
Key Tools and Frameworks
Reconnaissance & Scanning
Nmap, Shodan, Masscan, Nessus, OpenVAS
Web App & API Testing
Burp Suite Pro, ZAP, SQLmap, Dirb/Gobuster
Exploitation & Post-Exploitation
Metasploit, PowerShell Empire, Mimikatz, BloodHound