Penetration Testing

                 
–


                                  (Core Competencies)                              


Penetration testing is planned against agreed assets and objectives. Assessment areas can include web applications, networks, and identity systems. Testing is limited to the written scope, with findings prioritized by evidence, impact, and remediation effort.
Domain Expertise Active Directory (ADDS), Kerberos, NTLM
Assessment focus Configuration, access control, and vulnerability review
Tools Utilized BloodHound, Covenant/Empire, Burp Suite Pro, Custom Scripts
Targets Internal Networks, Web Apps, Cloud (Azure/AWS)
Malware Development and Penetration Testing
Ndato Jeanluck Penetration Testing

(Details)

Discovery maps the in-scope systems and identifies likely exposure paths. Where identity testing is authorized, review can cover directory relationships, access controls, and configuration weaknesses using controlled methods.
Validation remains within agreed safety limits and uses the minimum evidence needed to explain risk. Reporting provides reproducible findings, severity rationale, and remediation guidance; retesting can confirm fixes when included in scope.
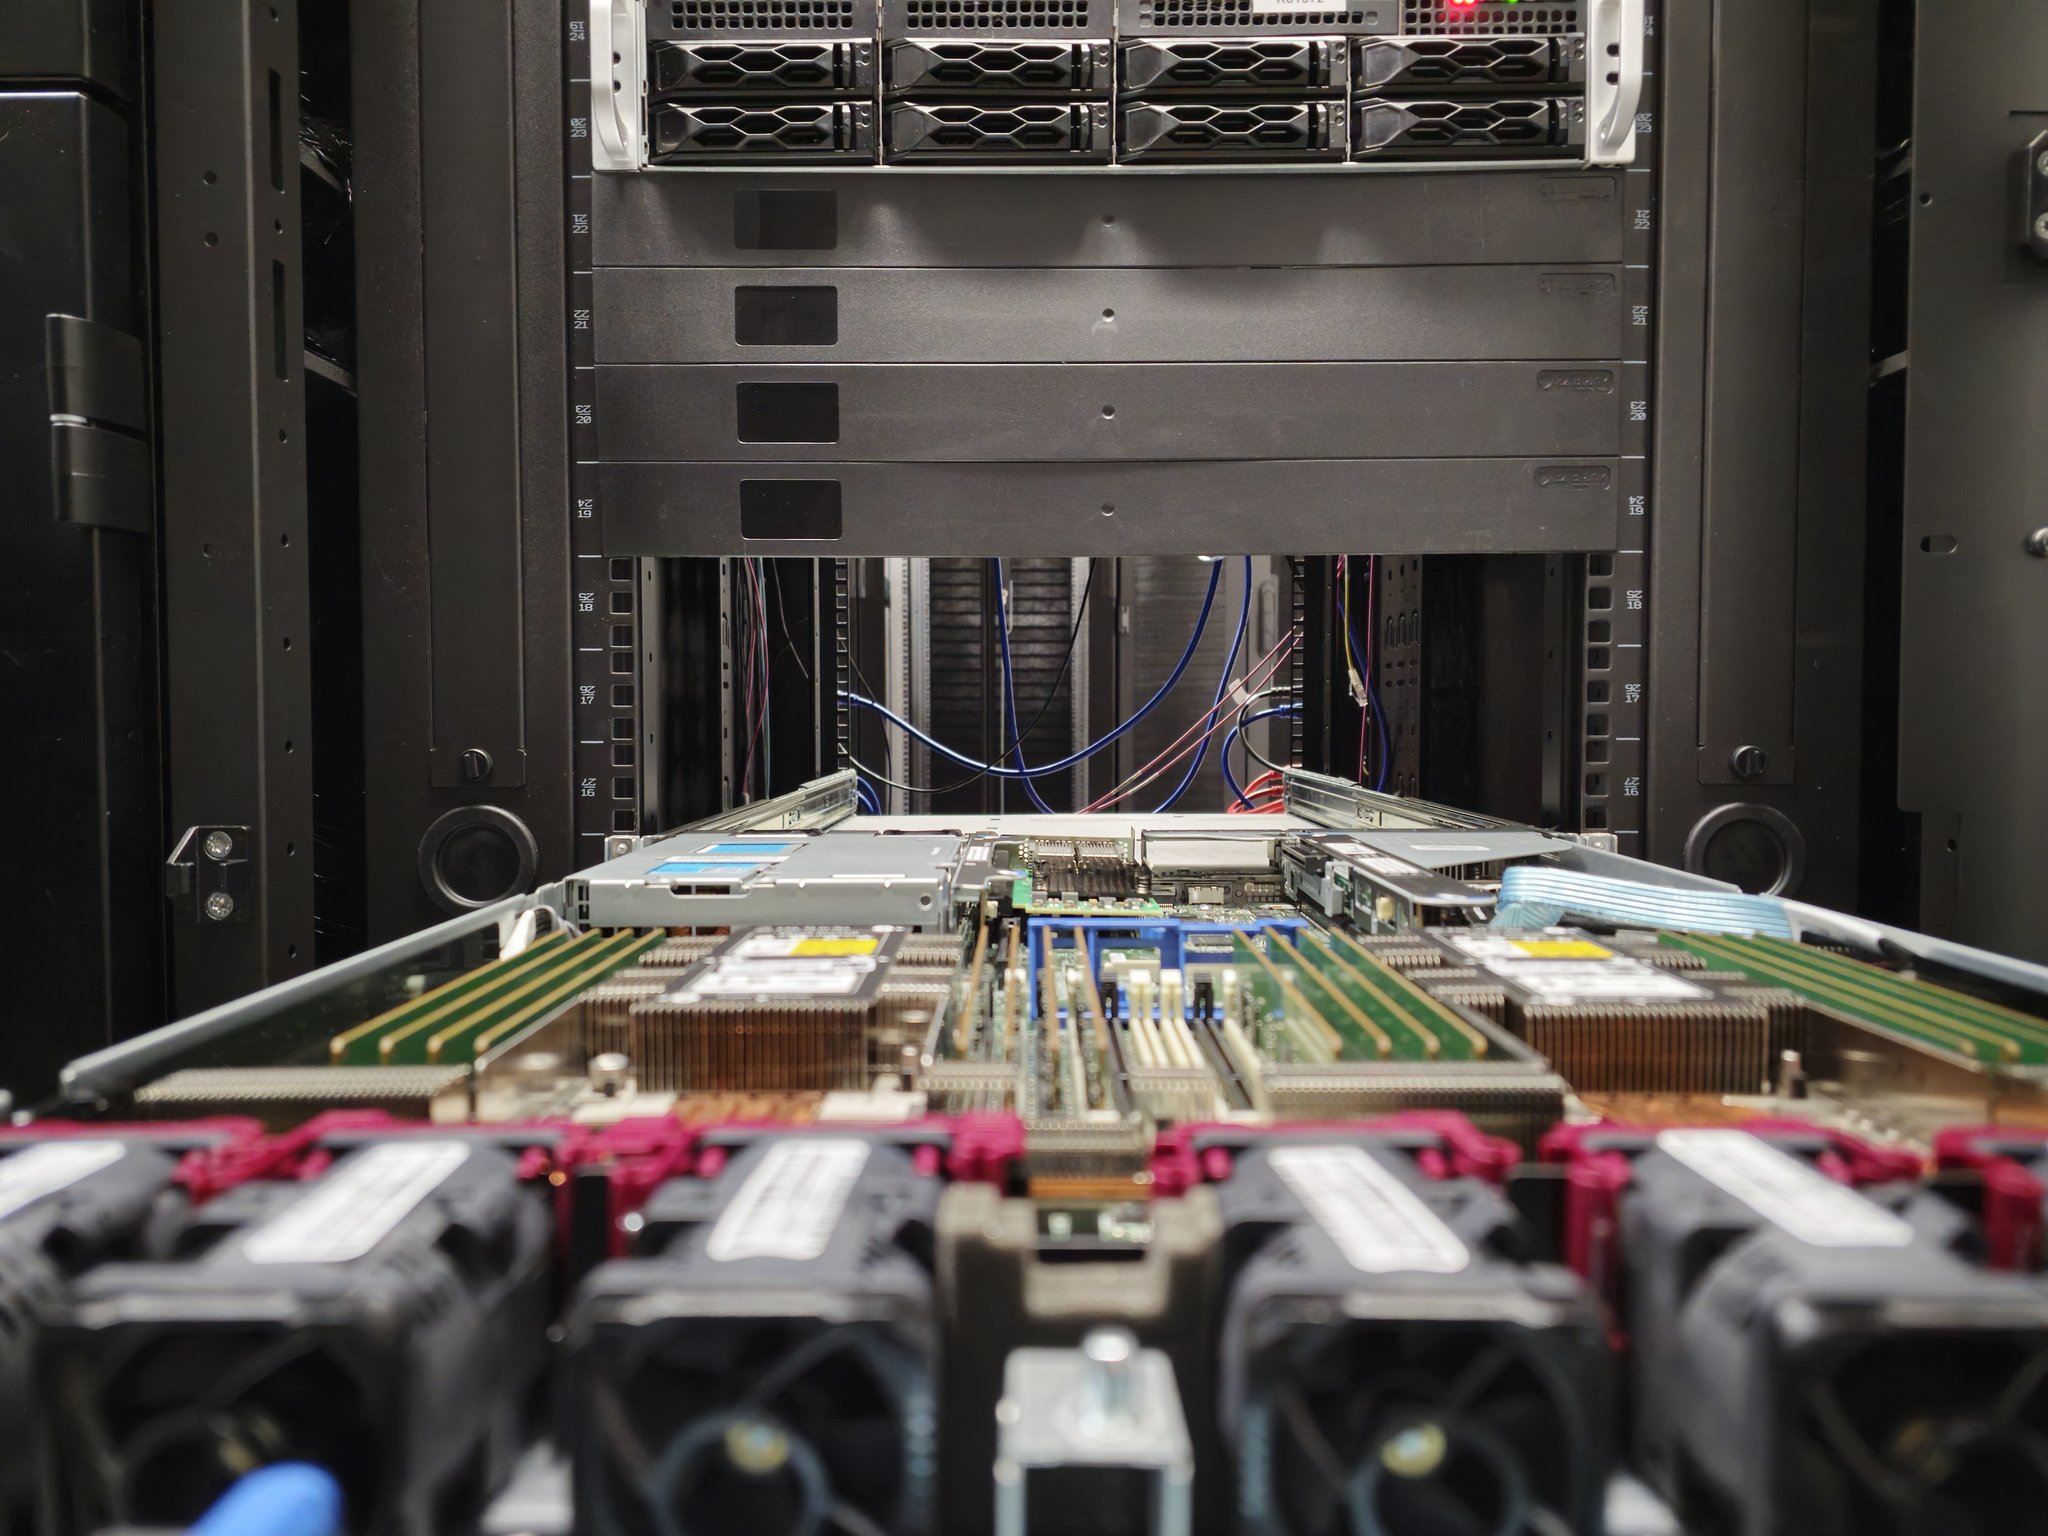
Penetration Testing Laboratory Setup
Red Team Network Assessment
Active Directory Attack Path
Command and Control Infrastructure
Vulnerability Exploitation Analysis
Internal Network Lateral Movement
Enterprise Security Assessment
Post Exploitation and Defense Evasion
Offensive Security Tooling and Payload


                                      (Technical Arsenal)                                  


Category
                 
Tools & Expertise


AD Post-Exploitation


BloodHound, PowerView, Mimikatz, Rubeus


Custom Tooling & Evasion


C#, Python, GoLang (Payload Dev), C2 Frameworks (e.g., Covenant)


Web Application Testing


Deep Fuzzing, Insecure Deserialization, API Security, Burp Suite Pro