Malware Analysis & Detection Research

–

(Specialized Focus)

This page describes malware analysis and controlled lab research: examining sample behavior, understanding persistence and evasion concepts, and translating observations into defensive detection ideas. Any testing uses isolated, authorized environments.
Core Languages C/C++, Assembly, Golang, Python
Target Platforms Windows Internals (PE/DLL), Linux, MacOS
Analysis areas Sample behavior, persistence concepts, detection
Goal Behavior analysis and defensive detection
Assembly and Polymorphic Code Architecture
Scutterspider Threat Group Emulation

(Development Cycle)

Analysis begins with safe handling, static inspection, and a controlled execution plan in an isolated lab. The goal is to understand observable behavior and document indicators that defenders can use.
Findings can be translated into detection logic, incident-response notes, and hardening recommendations. Research stays within authorized lab environments and avoids deployment against third-party systems.
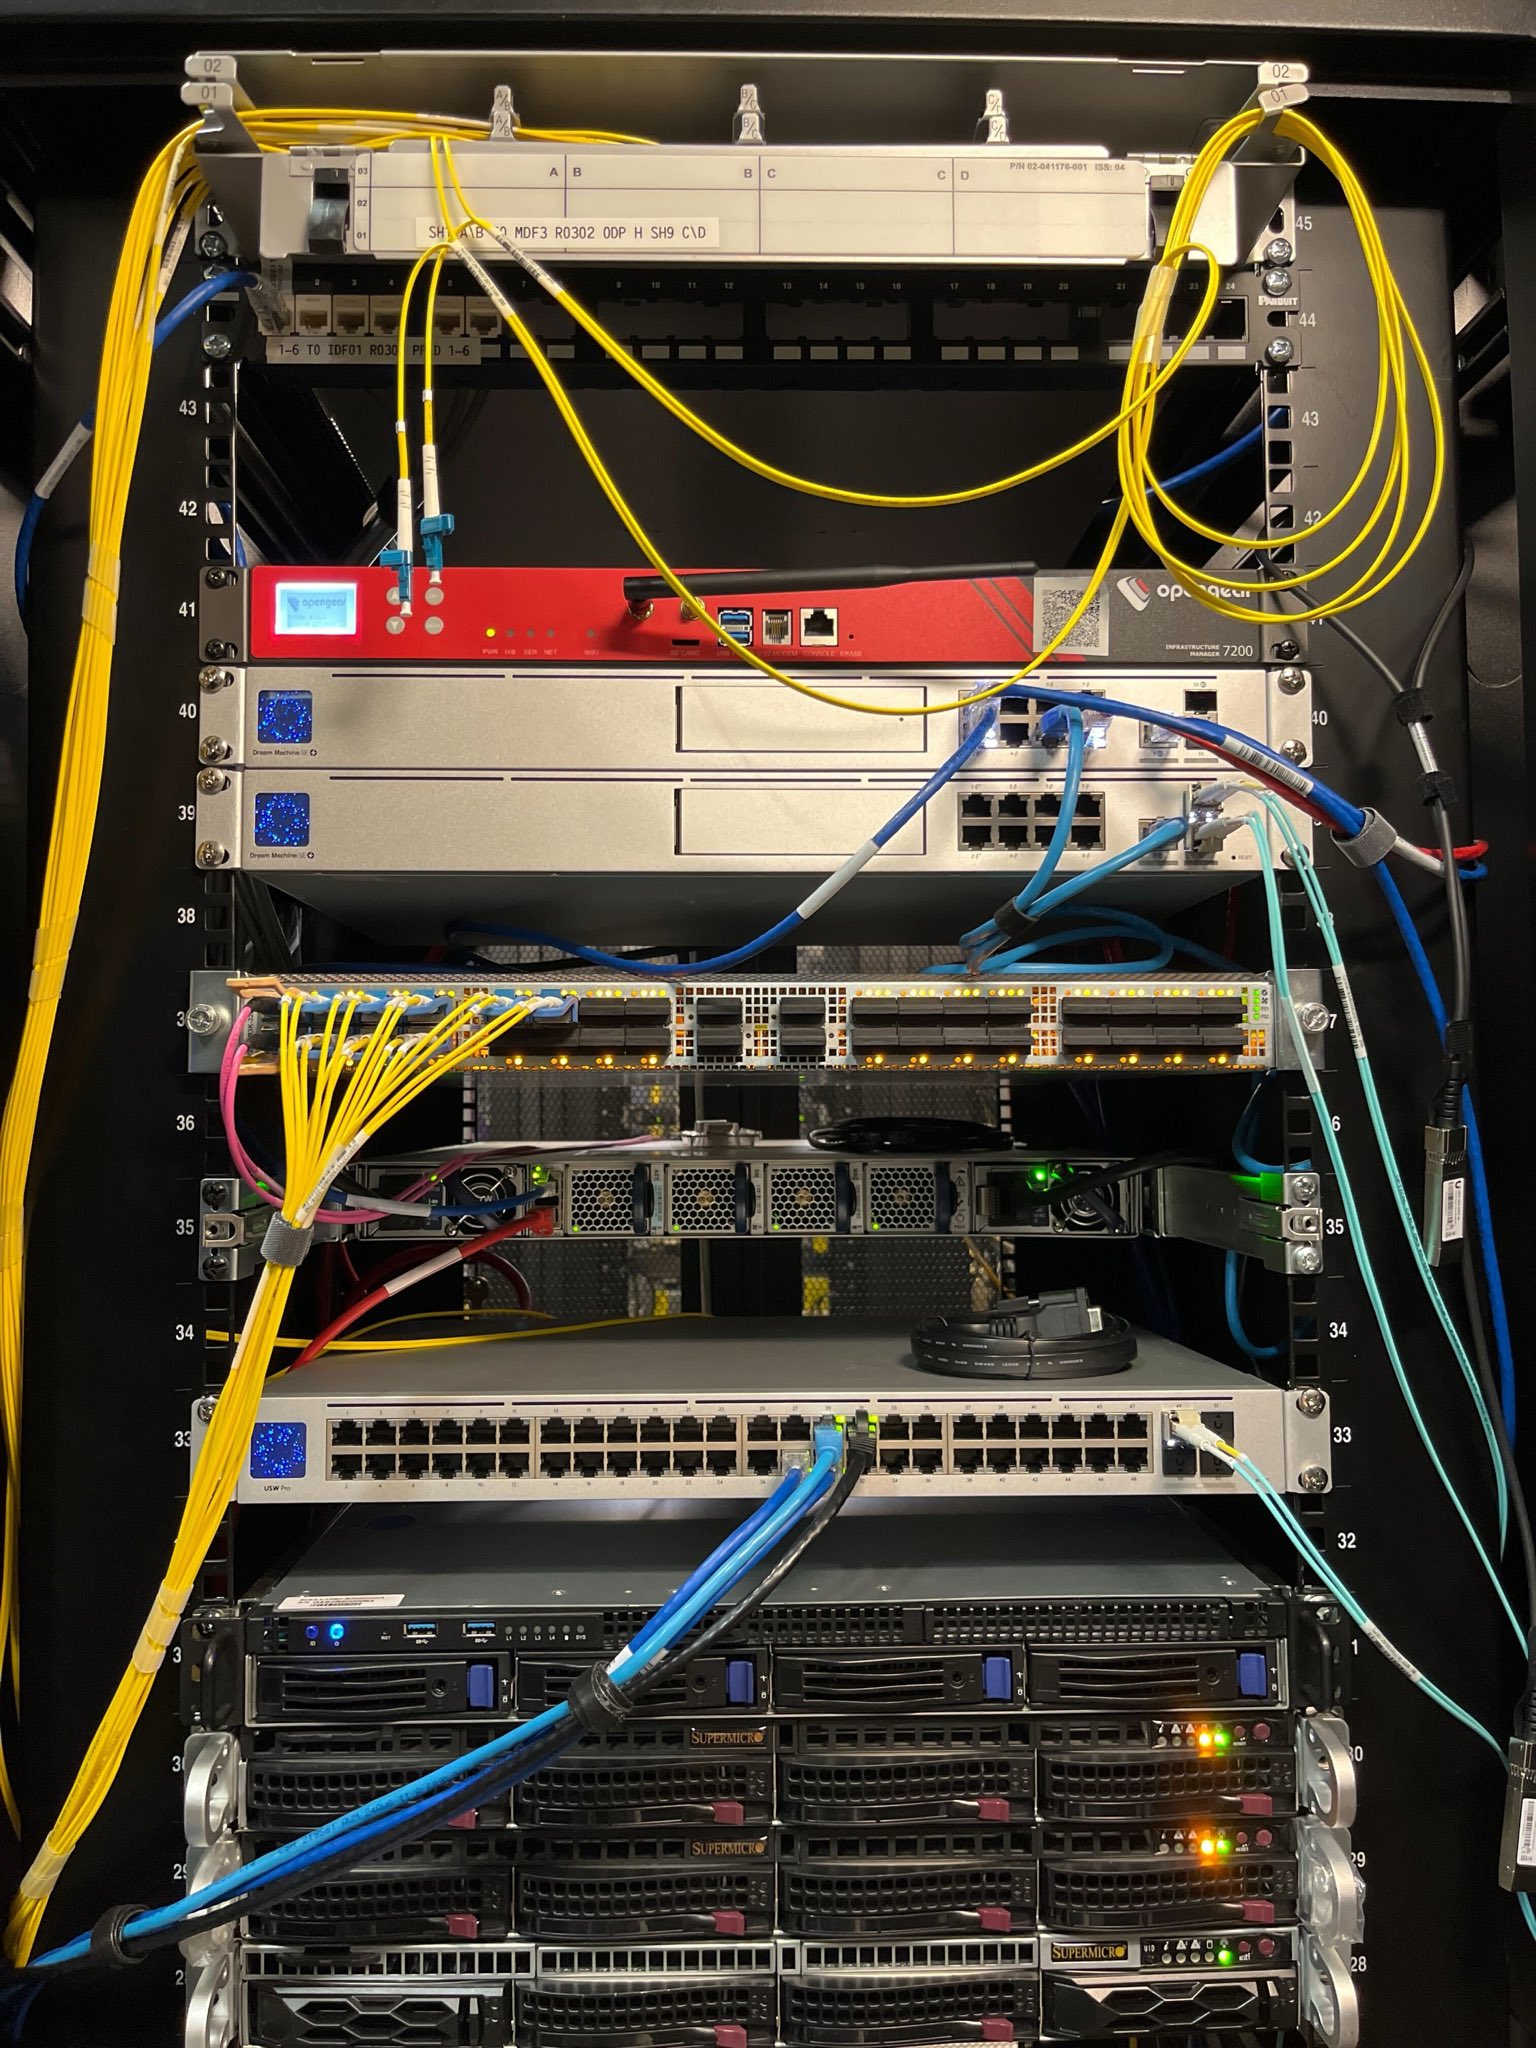
Network Infiltration and C2 Infrastructure
Malware Binary Disassembly and Analysis
Memory Injection and Process Hollowing Analysis
Payload Obfuscation and Compile Time Protection
Dynamic Hooking Bypass and Syscall Unhooking
Command and Control Channel Architecture
Red Team Defense Evasion Validation
Kernel Evasion and Callback Removal
Malware analysis and detection research

(Analysis Tools)

Analysis Category
Primary Tools / Frameworks Used
Static Analysis / Disassembly
IDA Pro / Ghidra, Cutter, radare2, PE-iD
Dynamic Analysis / Debugging
x64dbg, WinDbg, OllyDbg, Wireshark
Sandboxing / Automated Analysis
Cuckoo Sandbox, CAPE, Flare-VM, VMWare/VirtualBox